Otto Lehmann · 30 September 2026
Navigating Cross-Border Data Compliance Hurdles in Digital Note Management Systems
Digital note management systems now handle sensitive information across multiple jurisdictions, which creates layered compliance requirements for organizations that store and transfer user data internationally. Regulatory frameworks differ sharply between regions, so companies must map each data flow against local rules before deployment. Research from the European Data Protection Board indicates that standard contractual clauses remain the primary mechanism for lawful transfers outside the European Economic Area, yet these clauses demand ongoing risk assessments that many smaller platforms overlook during scaling phases.
Regulatory Frameworks Across Regions
Countries enforce distinct data protection statutes that affect how note management platforms process and store content, and observers note that organizations often face simultaneous obligations under several laws at once. The EU General Data Protection Regulation requires explicit consent or legitimate interest justification for cross-border transfers, while Canada's Personal Information Protection and Electronic Documents Act emphasizes accountability when data moves beyond national borders. Australia's Privacy Act adds another layer by mandating notification of eligible data breaches within tight timeframes, and companies that fail to align these standards encounter enforcement actions that disrupt service availability.
Starting in September 2026, updated provisions in several bilateral data transfer agreements will introduce mandatory encryption audits for cloud-based note services, according to announcements from regulatory bodies in multiple jurisdictions. These changes build on existing adequacy decisions and force providers to demonstrate technical safeguards before any data leaves its country of origin. Data shows that platforms using end-to-end encryption already meet many of these forthcoming requirements, whereas legacy systems relying on server-side access struggle to adapt without significant re-architecture.
Data Transfer Mechanisms and Their Limitations
Organizations rely on approved transfer tools such as binding corporate rules, standard contractual clauses, and certification schemes, yet each mechanism carries practical constraints when applied to collaborative note platforms. Binding corporate rules demand internal policies that satisfy multiple supervisory authorities, a process that typically takes eighteen to twenty-four months for approval. Standard contractual clauses work faster but require supplementary measures like data mapping and impact assessments whenever a destination country lacks an adequacy finding.
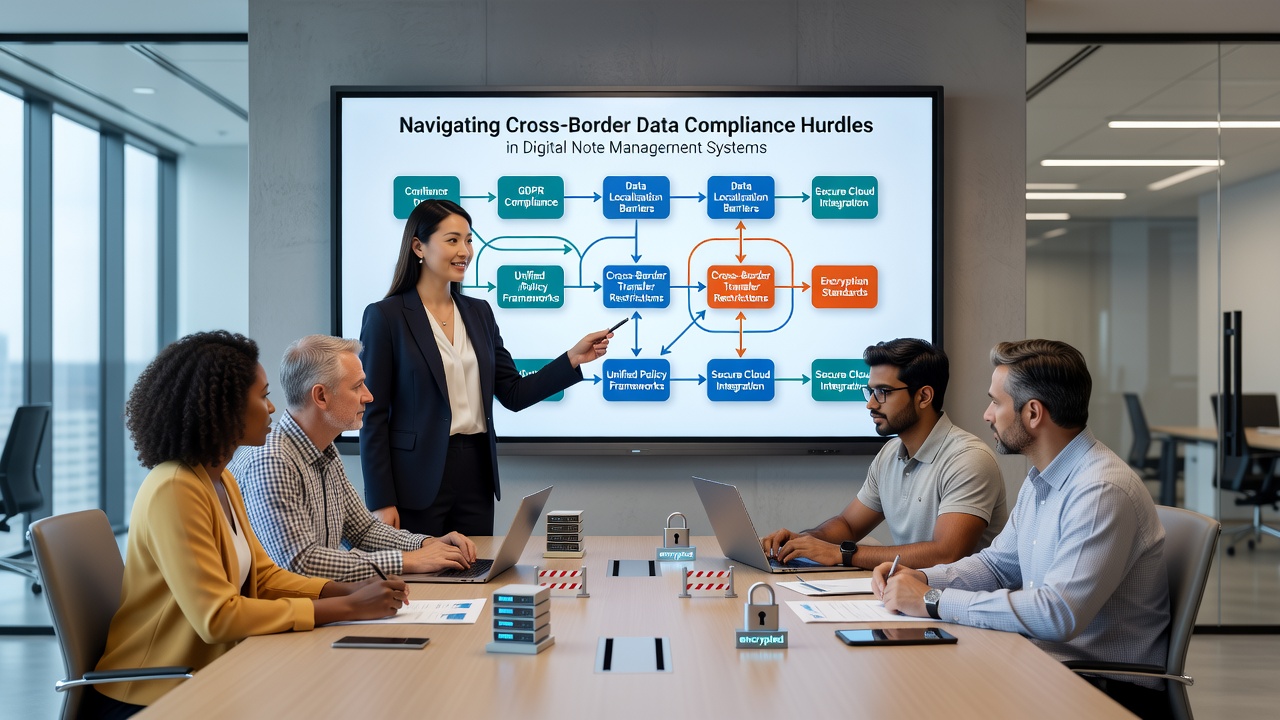
One study from the Organisation for Economic Co-operation and Development revealed that note management services frequently store metadata in different regions than user content, which complicates compliance because metadata can still qualify as personal data under most statutes. Transfers that appear routine can trigger additional scrutiny when users collaborate across borders in real time, since each participant location may impose separate localization rules. Experts observe that without automated compliance tooling, teams spend disproportionate resources on manual documentation rather than core product development.
Operational Challenges in Note Platforms
Note management systems generate continuous data streams through features like real-time synchronization, shared workspaces, and version histories, all of which create persistent compliance obligations. When a user in one country shares a note with collaborators elsewhere, the platform must determine the lawful basis for every transfer instance and retain records that demonstrate ongoing adherence. Research indicates that encryption key management becomes especially complex when keys must remain under the control of entities in specific jurisdictions to satisfy data residency statutes.
Platforms also confront requests from law enforcement agencies in different countries, and these requests sometimes conflict when one jurisdiction demands access while another prohibits disclosure. Organizations that maintain clear data access policies and publish transparency reports help users understand how such conflicts are resolved, although the volume of requests continues to rise each year. Figures from government transparency portals show that note service providers received thousands of such demands annually across major markets, underscoring the need for standardized response protocols.
Strategies That Reduce Compliance Friction
Successful implementations begin with comprehensive data inventories that classify information by sensitivity and jurisdiction before any transfer occurs. Teams then select hosting regions that minimize the number of cross-border movements while still supporting global user bases. Many providers now deploy regional data centers paired with automated policy engines that apply the strictest applicable rule set to each note or attachment.
Training programs that keep legal and engineering staff aligned on evolving requirements further reduce risk, since regulatory updates often arrive with short implementation windows. Certification under recognized frameworks such as ISO 27701 provides external validation that internal controls meet international benchmarks, and several note platforms have leveraged these certifications to streamline vendor assessments from enterprise customers.
Conclusion
Cross-border data compliance in digital note management systems requires continuous attention to shifting regulations and technical controls that adapt to multiple legal regimes simultaneously. Organizations that invest early in mapping, encryption, and policy automation position themselves to handle new obligations that take effect in September 2026 and beyond, while those that treat compliance as a one-time project face repeated disruptions. The combination of regulatory enforcement actions and user expectations for data protection means that robust transfer mechanisms remain essential infrastructure for any platform operating internationally.